BattleTest
Autonomous Security Testing
Continuous security
on autopilot.
BattleTest verifies every code change and probes live applications — catching vulnerabilities before attackers reach them.
Identify flaws
→
Validate exploits
→
Deliver fixes
battletest.dev
01 /The Exposure Problem
Companies expanded online fast. Most still have no one running security.
$10.3B
Total cybercrime losses reported to the FBI in 2022. Attackers moved off hardened Fortune 500 targets onto startups, regional infrastructure, and mid-market.
(FBI Internet Crime Report 2022 — reported US losses)
Widespread disruption.
A single leaked credential or unpatched system can freeze port operations, halt legal proceedings, or take down health services for weeks.
No time to check.
Teams ship constantly to stay competitive — leaving little room or budget for manual security review.
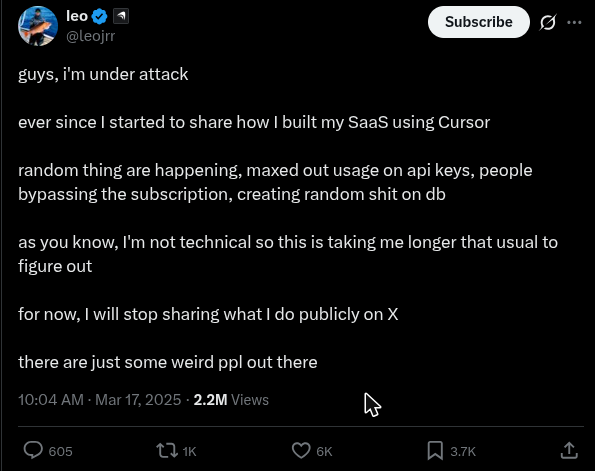
@leojrr · X · 2.2M views — a non-technical founder, live-breached
Publicly reported breaches since 2020 · Nigerian names in red
Nigeria: ₦17.67bn lost to bank fraud in 2023 (Banks lose N18bn to fraudsters in 2023 — NIBSS, The Punch, Apr 2024)
02 /The AI Velocity Gap
Attackers automated. Defense is still a manual code review.
SECONDSThreat actors scan thousands of public endpoints, hunt API flaws, and attempt exploits within seconds.
45%Of AI-generated code introduced a known security weakness — measured across 100+ models, shipped at machine speed. (Veracode GenAI Code Security Report, 2025)
THE GAPAnnual and semi-annual pentests are obsolete when software goes live daily.
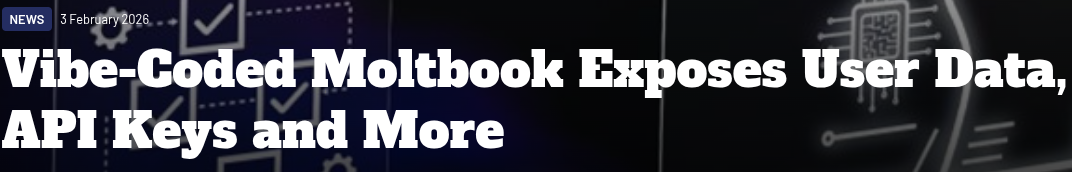
Infosecurity Magazine · Feb 2026 — a vibe-coded app leaked 30,000 emails and 1.5M API tokens.
03 /False Positive Overload
Too many false alarms. So teams mute security entirely.
Legacy tooling
"Dependabot is a noise machine."
Filippo Valsorda · Feb 2026
Static scanners spew theoretical warnings until developers switch them off. Point-in-time audits go stale on the next merge.
The BattleTest approach
"Proof of exploitability reduces noise and increases SNR."
ngneer · Hacker News
Every suspected bug is fired in an isolated sandbox to confirm a real exploit exists. Developers get high-confidence findings — with verifiable proof and a suggested fix.
04 /Product Architecture
Review code as it's written. Test the app as it runs.
PHASE 1Code reviewdevelopment
Evaluates pull requests directly in the repository workflow.
Filters harmless warnings and posts suggested fixes inline on the developer's PR.
PHASE 2Live testingstaging
Deploys an autonomous agent to probe staging and test reachable routes safely.
Requires explicit human approval before any high-impact action runs.
Can be self-hosted. Deploy in your own cloud so source code and customer data never leave your environment.
05 /Feature 01 — Multi-File Code Review
Full repository context on every change.
01
Repository-wide awareness
Traces data flows across interconnected files instead of inspecting code in isolation.
02
Business-logic flaws
Catches complex authorization issues, broken access controls, and hardcoded secrets.
03
Automated pipeline guards
Integrates with CI/CD to stop unsafe code from merging into production.
Live Demo /Code Review
Watch it hunt — then gate the merge.
real review · digitaldrreamer/paylane-api#1
Real run — findings stream in, verify in sandbox, verdict lands at Risk 100/100 and gates the merge.
07 /Feature 02 — Automated Staging Pentests
Autonomous agents against live staging.
01
Target mapping
Discovers exposed API endpoints, subdomains, and login portals automatically.
02
Adaptive testing
Simulates real-world attack techniques instead of checking static vulnerability lists.
03
Operator control
Teams set strict boundaries or steer agent focus with clear guidelines.
04
Compliance artifacts
Generates clean execution logs suitable for SOC 2 and ISO 27001 audits.
Live Demo /Agent Session
It stops and asks before it escalates.
human-in-the-loop control log
Real run — parallel agents map, probe and prove a live SQL injection, pausing for human approval before escalation.
09 /Traction
8 engineering teams onboarded, plus inbound enterprise demand.
8
active teams in 2 weeks
reached entirely through word of mouth
Enterprise pipeline
Inbound pilot request from a payment-software company for a self-hosted enterprise deployment.
Deployment advantage
Regulated organizations can't upload sensitive source code to external clouds — a self-hostable architecture fits where others can't go.
10 /Market Context
A $5.5B pentest market moving to continuous testing.
$2.7B
→
$5.5B
Global penetration-testing market size — 2026 → 2031 forecast (~15% CAGR). Growth driven by tightening compliance requirements. (Mordor Intelligence, Penetration Testing Market, 2026)
~30% financial services
Financial services (BFSI) is the single largest buyer segment of the pentest market — matching our primary inbound demand. (Mordor Intelligence, Penetration Testing Market, 2026 — BFSI share 28.68%)
Annual audits to daily testing
Buyers are shifting to automated testing embedded in the development cycle.
"Having to devote $60k to a pentest before even getting off the ground would have sunk Apple."
sillysaurus3 · Hacker News
"This killed a deal for us — a customer walked because we couldn't produce a SOC report."
daniel_lozano · Indie Hackers
11 /Capital & Strategy
$250k
allocated across four priorities40%$100k
Product engineering
Bug bounties and cyber challenges to validate AI accuracy.
25%$62.5k
Marketing & free tier
Brand reach and visibility on public repositories.
20%$50k
Buffer
Reserved for unexpected expenses and runway.
15%$37.5k
Go-to-market
Convert early pilots into annual enterprise agreements.
The Moat
Every test run refines BattleTest's verification harness — accuracy compounds and false alarms fall as usage grows. The advantage widens with every review.
BattleTest
Security review on every
pull request.
Continuous testing for code and live apps — with proof, fixes, and a human in the loop.
battletest.dev
$250k · seed the verification advantage